Cloud Security Engineering
We help organizations evaluate cloud risk, audit IAM privileges, scan infrastructure code for vulnerabilities, and meet compliance benchmarks without slowing down delivery velocity.
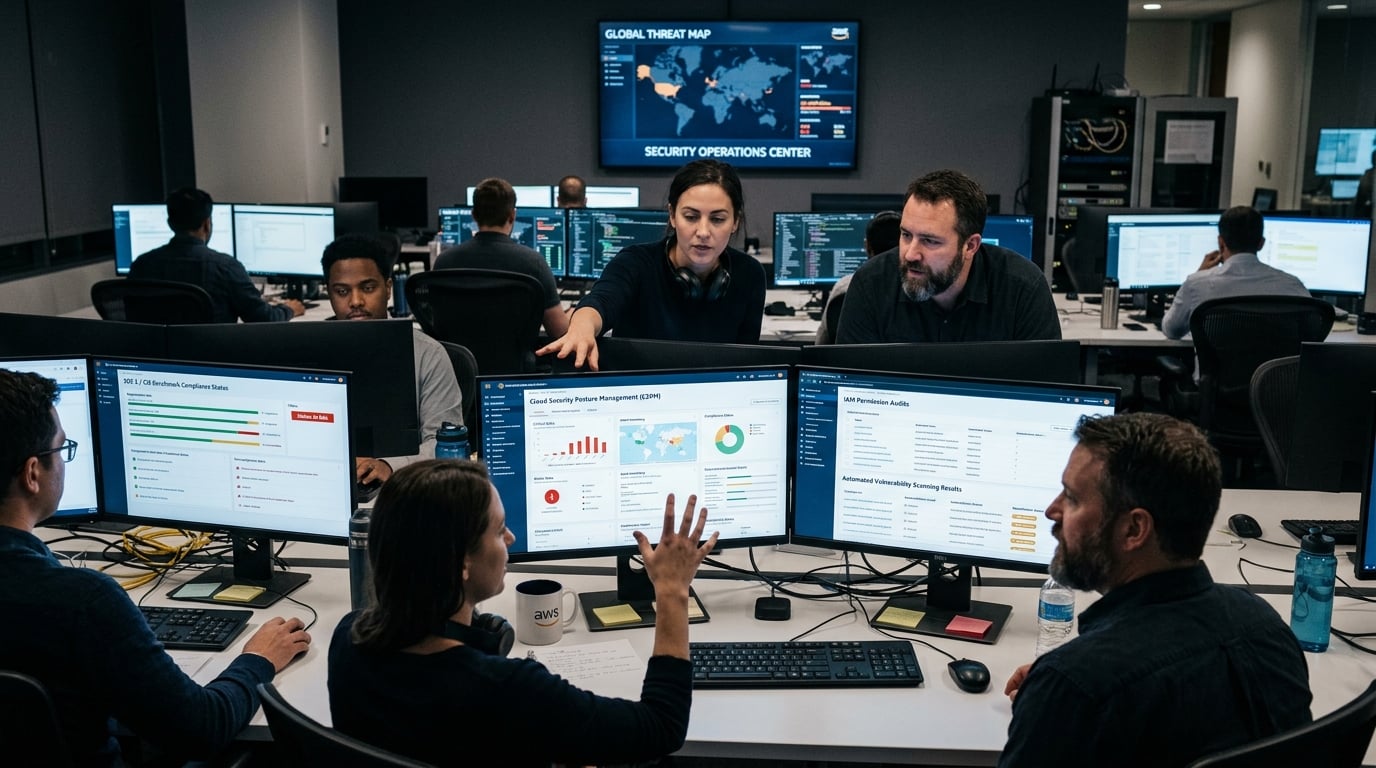
Harden multi-cloud environments and embed security into daily development.
Cloud security is an active operational discipline, not an annual audit checkbox. We audit IAM least-privilege boundaries, scan infrastructure as code for misconfigurations, and implement continuous posture monitoring that keeps environments hardened without impeding developer shipping velocity.
Book a 30-minute security call
We can scope a focused architectural discussion around your current cloud footprint, delivery pipelines, and where the highest-value security improvement sits.
The core workstreams inside this service line.
AWS and cloud security assessments
Infrastructure hardening and remediation
DevSecOps guardrails
Compliance mapping and continuous posture monitoring
A delivery sequence designed to move from assessment to measurable outcome.
Assess the attack surface, delivery model, and current control coverage.
Prioritise the highest-risk infrastructure, identity, and pipeline gaps.
Implement repeatable controls and monitoring instead of one-off fixes.
Use CloudGuardian and engineering runbooks to keep posture current over time.
Typical technologies involved in this service.
Cloud Security Assessment
The customer needed a broad security review of critical AWS-hosted services, along with actionable remediation priorities and compliance visibility.
Actionable remediation roadmap for cloud security posture
Questions teams often ask before starting.
Clear, transparent answers about engagement model, deliverables, and production safety.